Hi everyone,
I’m running into an issue with our Endpoint Agent configuration where event though we have the path $LocalAppData$\* set to ignore, the agents are still generating incidents for application file access events in that path
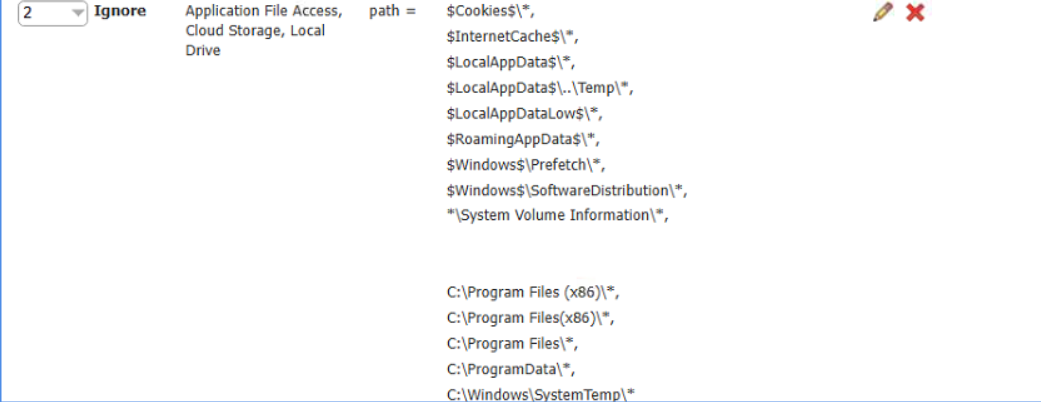
For example, these paths are still triggering incidents:
C:\Users\<user>\AppData\Local\Packages\MSTeams_8wekyb3d8bbwe\LocalCache\...
D:\Users\<user>\AppData\Local\Packages\MSTeams_8wekyb3d8bbwe\LocalCache\...
C:\Users\<user>\AppData\Local\Publishers\8wekyb3d8bbwe\TeamsSharedConfig\tma_settings.json
C:\Users\<user>\AppData\Local\Microsoft\Office\16.0\Floodgate\Outlook.Settings.json
It seems like the $LocalAppData$ isn't resolving properly, or the single wildcard \* isn't recursing deeply enough into the nested Office/Teams directories.
Has anyone else dealt with this behavior?