Original Message:
Sent: Aug 14, 2026 07:09 PM
From: Jose Romero
Subject: NFA stacked Protocol Trend - Out without graph
Dear Justin, the admin shared the following with me:
how configuration services flow-monitoring
Aug 14 16:13:55
version-ipfix {
template ipv6-ipfix {
flow-active-timeout 60;
flow-inactive-timeout 60;
template-refresh-rate {
packets 1000;
seconds 30;
}
option-refresh-rate {
packets 500;
seconds 60;
}
ipv6-template;
}
template ipv4-ipfix {
flow-active-timeout 60;
flow-inactive-timeout 60;
template-refresh-rate {
seconds 30;
}
option-refresh-rate {
seconds 30;
}
ipv4-template;
}
}
In addition, please request the following:
show configuration interfaces et-4/0/5 unit 222
Aug 14 16:19:43
description "CONEXION A UNINET | Trafico telcel_ipcorp";
vlan-id 222;
family inet {
sampling {
input;
output;
}
address 187.219.83.214/30;
#####
show configuration forwarding-options
Aug 14 16:15:22
sampling {
input {
rate 10000;
run-length 10;
}
instance {
INST_FPC4 {
input {
rate 10000;
}
family inet {
output {
flow-server 10.8.9.168 {
port 9995;
version-ipfix {
template {
ipv4-ipfix;
}
}
}
inline-jflow {
source-address 10.255.1.67;
}
}
}
family inet6 {
output {
flow-server 10.8.9.168 {
port 9995;
version-ipfix {
template {
ipv6-ipfix;
}
}
}
inline-jflow {
source-address 10.255.1.67;
}
}
}
}
}
}
hash-key {
family inet {
layer-3;
layer-4;
}
family mpls {
label-1;
label-2;
payload {
ip;
}
}
}
{master}
Original Message:
Sent: Aug 14, 2026 02:55 PM
From: Justin Signa
Subject: NFA stacked Protocol Trend - Out without graph
Jose,
I think the INPUT data is now just showing up as OUPUT data.
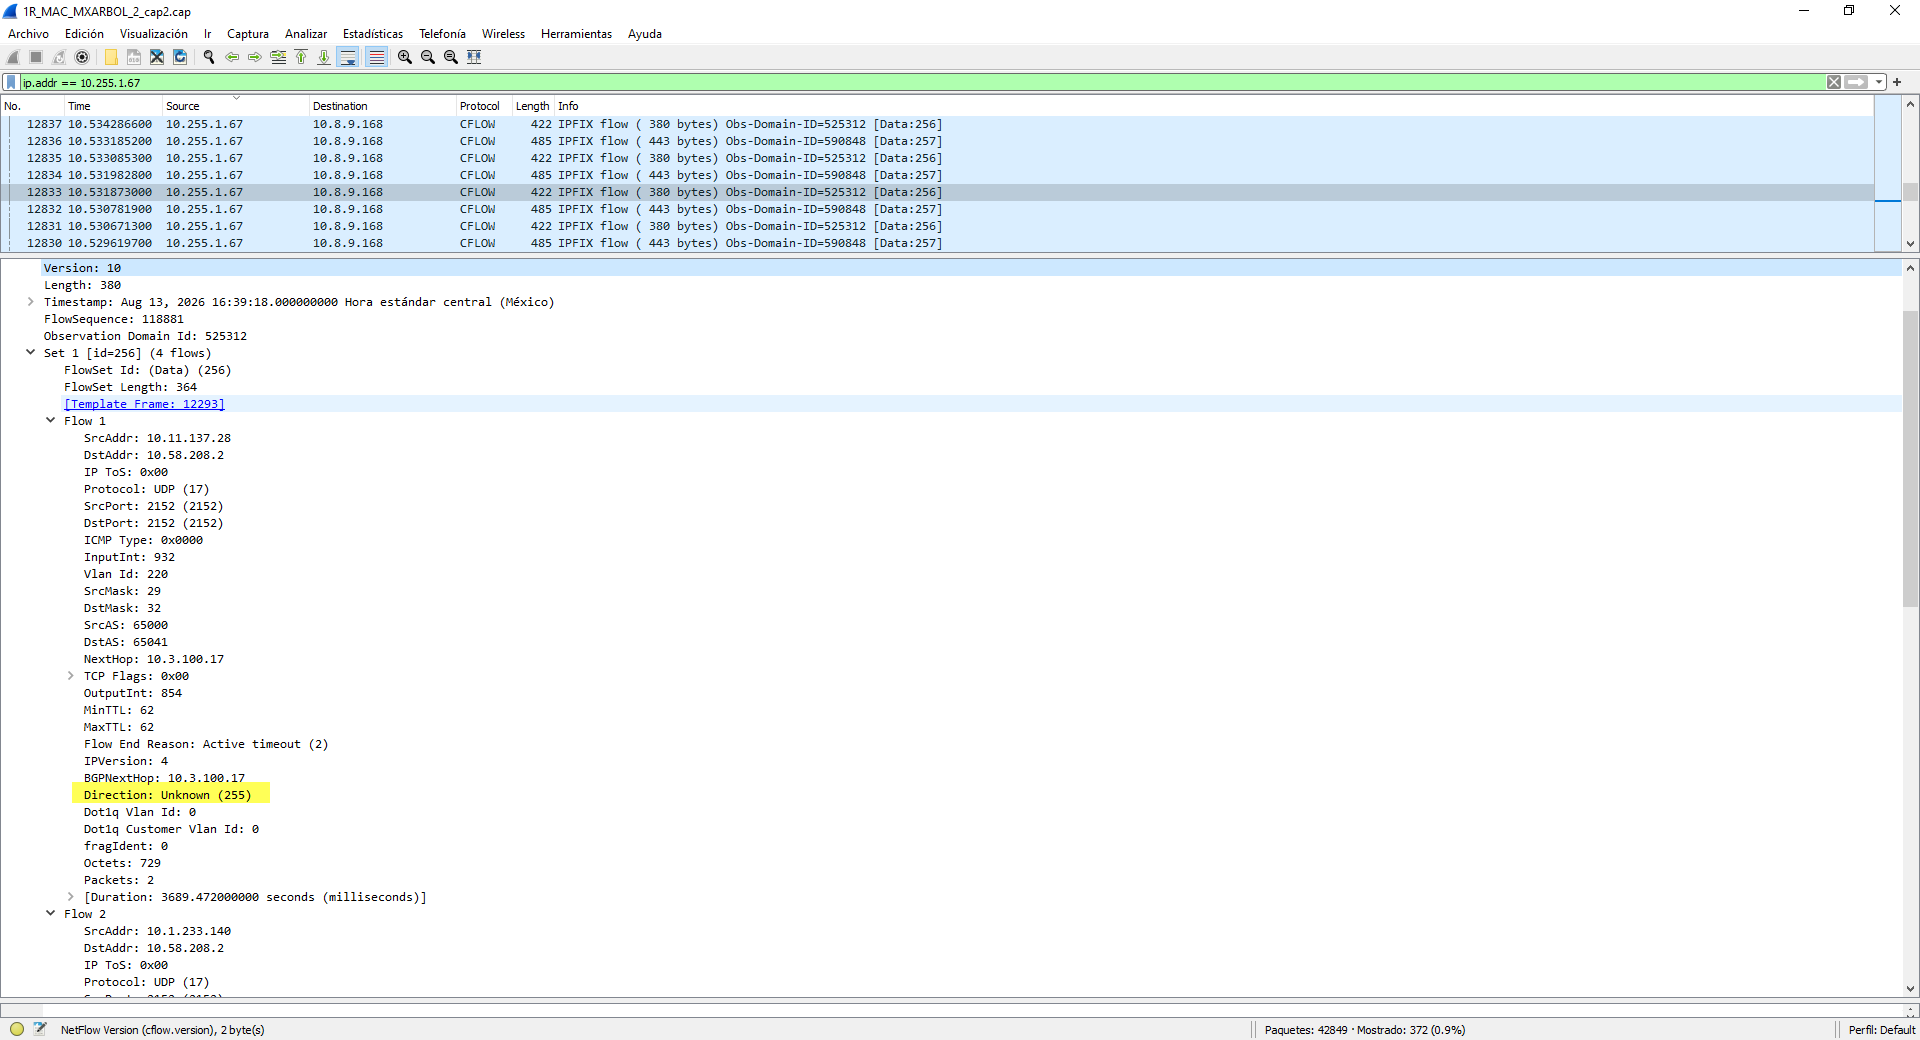
I think the flow-direction field neds to be removed. That shouldn't be needed if configured properly.
We are not juniper experts but it would probably be something like this:
delete services flow-monitoring version-ipfix template ipv4-ipfix flow-direction
delete services flow-monitoring version-ipfix template ipv6-ipfix flow-direction
You need to configure output monitoring on the interfaces likely.
Can you run: show configuration services flow-monitoring
Original Message:
Sent: Aug 14, 2026 02:13 PM
From: Jose Romero
Subject: NFA stacked Protocol Trend - Out without graph
Thanks for the guide, Justin; it was very helpful. The user configured IPFIX on the device as you suggested, but now the opposite has happened: it stopped displaying IN graphs.
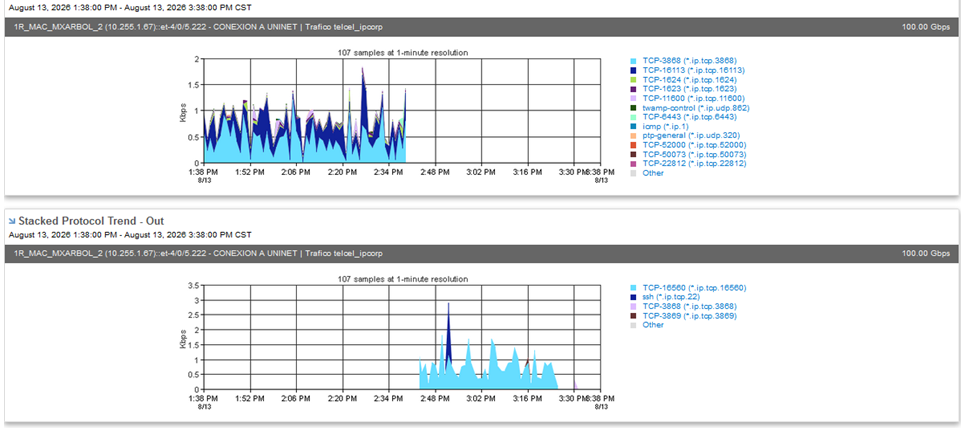
I asked the user for the configuration, and they shared this with me.
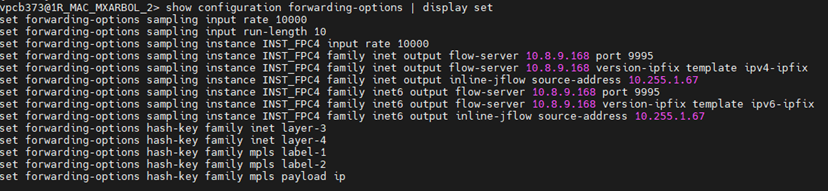
I'm not sure if this is correct; furthermore, when checking the packets sent by IPFIX, I found that the field that should indicate whether it is ingress or egress appears as "unknown."
I think it's a device configuration issue.
Original Message:
Sent: Aug 12, 2026 03:18 PM
From: Justin Signa
Subject: NFA stacked Protocol Trend - Out without graph
Yeah this Juniper is configured for both IPFIX and v5. On top of that it is only set for input data.
You need to remove te v5 flows and set it up for egress (see this example below):
sampling {
input {
rate 10000;
run-length 10;
}
output { /* <-- ADDED: Global egress sampling */
rate 10000;
run-length 10;
}
family inet {
output {
flow-inactive-timeout 60;
flow-active-timeout 60;
flow-server 10.8.9.168 {
port 9995;
no-local-dump;
source-address 10.255.1.67;
version-ipfix { /* <-- CHANGED: Replaced version 5 */
template {
ipv4-ipfix;
}
}
}
}
}
instance {
INST_FPC4 {
input {
rate 1;
}
output { /* <-- ADDED: Egress sampling for FPC4 */
rate 1;
}
family inet6 {
output {
flow-server 10.8.9.168 {
port 9995;
version-ipfix {
template {
ipv6-ipfix;
}
}
}
}
inline-jflow {
source-address 10.255.1.67;
}
}
}
}
}
hash-key {
family inet {
layer-3;
layer-4;
}
family mpls {
label-1;
label-2;
payload {
ip;
}
}
}
Even thought the above example will take care of the global configuration,don't forget to add sampling with output to your interfaces or it will continue to export just ingress data.
I also see you have ipv6 monitoring on. If this is needed ensure that the IPFIX template is set for IPv4 and IPv6 if this is what you want.
Original Message:
Sent: Aug 12, 2026 02:26 PM
From: Jose Romero
Subject: NFA stacked Protocol Trend - Out without graph
Dear Justin, thank you for the response, I understand that they should only send one protocol at a time, and that the best option to ask to configure Netflow sending is version 9, is this correct?
The admin shared the configuration with me
sampling {
input {
rate 10000;
run-length 10;
}
family inet {
output {
flow-inactive-timeout 60;
flow-active-timeout 60;
flow-server 10.8.9.168 {
port 9995;
no-local-dump;
source-address 10.255.1.67;
version 5;
}
}
}
instance {
INST_FPC4 {
input {
rate 1;
}
family inet6 {
output {
flow-server 10.8.9.168 {
port 9995;
version-ipfix {
template {
ipv6-ipfix;
}
}
}
inline-jflow {
source-address 10.255.1.67;
}
}
}
}
}
}
hash-key {
family inet {
layer-3;
layer-4;
}
family mpls {
label-1;
label-2;
payload {
ip;
}
}
}
{master}
Original Message:
Sent: Aug 12, 2026 09:24 AM
From: Justin Signa
Subject: NFA stacked Protocol Trend - Out without graph
This device is 100% misconfigured. You have traditional netflow commands (ip flow ingress) configured with flexible netflow (flow records / exporters / monitors).
This is resulting in the v5 flows and v10 flows both being exported from the device.
Original Message:
Sent: Aug 11, 2026 03:45 PM
From: Jose Romero
Subject: NFA stacked Protocol Trend - Out without graph
Dear Justin, I'm sharing the traffic capture with you. I'm wondering if ipfix and netflow v5 are causing the problem, as I see them sending messages. I'm not sure if this is the issue, but I also see "out" in both cases.
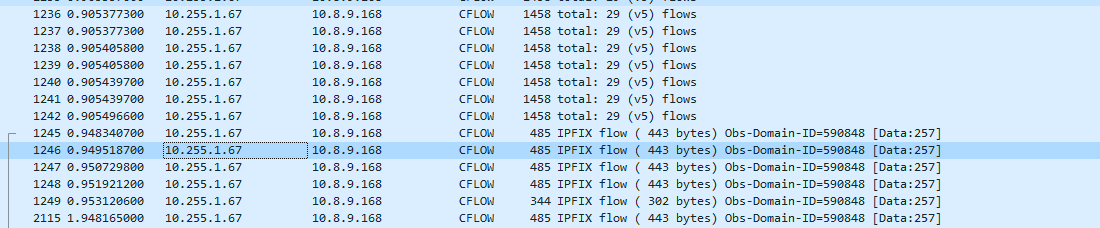
ip 10.255.1.67
Original Message:
Sent: Aug 10, 2026 03:07 PM
From: Justin Signa
Subject: NFA stacked Protocol Trend - Out without graph
Jose,
Is it that you are not seeing out traffic AT ALL (Protocol / Hosts / Conversations) ? Or is it just flows outbound which are not working?
Thanks,
Justin Signa
Original Message:
Sent: Aug 10, 2026 03:01 PM
From: Jose Romero
Subject: NFA stacked Protocol Trend - Out without graph
Thanks for the reply; I am waiting for permission to capture the traffic. The administrator has sent me the following information about the interface.
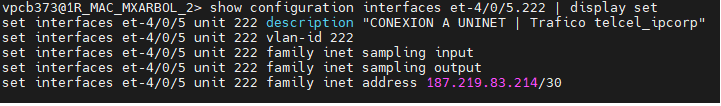
The device model is: MX960
The administrator notes that outbound traffic on the interface exceeds inbound traffic, so this is something that should be monitored; however, in NFA, we only see graphs for inbound traffic.
Original Message:
Sent: Aug 10, 2026 10:01 AM
From: Justin Signa
Subject: NFA stacked Protocol Trend - Out without graph
Jose,
For something like this I would open a support ticket and upload a 15 minute packet capture filtered to the the specific device on port 9995 from the NFA Harvester.
https://knowledge.broadcom.com/external/article/11095/how-can-i-determine-if-a-netflow-enabled.html
Thanks,
Justin Signa