Symantec IGA

 View Only

  • 1.  IGA 15.0

    Posted Sep 04, 2025 06:57 AM

    We are very interested to hear if anyone has upgraded or plans to upgrade from 14.5 SP1 CHF1 to 15.0.

    We are currently running on virtual appliances and are looking into what will be required to successfully migrate a heavily customized IGA 14.5.1 CHF1 to 15.0.

    Mogrify will do a lot of the work capturing the configuration, but the documentation is clear that there will be configuration that needs to be moved manually.  It's less clear on what this configuration is (although it may be there in the detail of each component) - any high level suggestions about what is expected to not be covered by Mogrify would be very much appreciated.

    We also have many customized reports, which are a critical component of our deployment, and it will be interesting hear how it has gone for anyone else who has customized reports and is moving to 15.0.

    Adrian


    -------------------------------------------


  • 2.  RE: IGA 15.0

    Broadcom Employee
    Posted Sep 05, 2025 01:09 AM

    Hello Adrian,

    The following page gives an overview of the configurations that Mogrify handles and what needs to be manually handled post migration.

    https://techdocs.broadcom.com/us/en/symantec-security-software/identity-security/iga-xpress/1-0/migrate/plan-the-migration.html

    Shamlee

    -------------------------------------------


  • 3.  RE: IGA 15.0

    Posted Sep 05, 2025 03:50 AM

    Hi,

    We attempted to migrate from VApp to v15, but ran into an issue. All services have started, but we are unable to log in to Identity Manager. When trying to log in, it shows an "Internal Server Error."
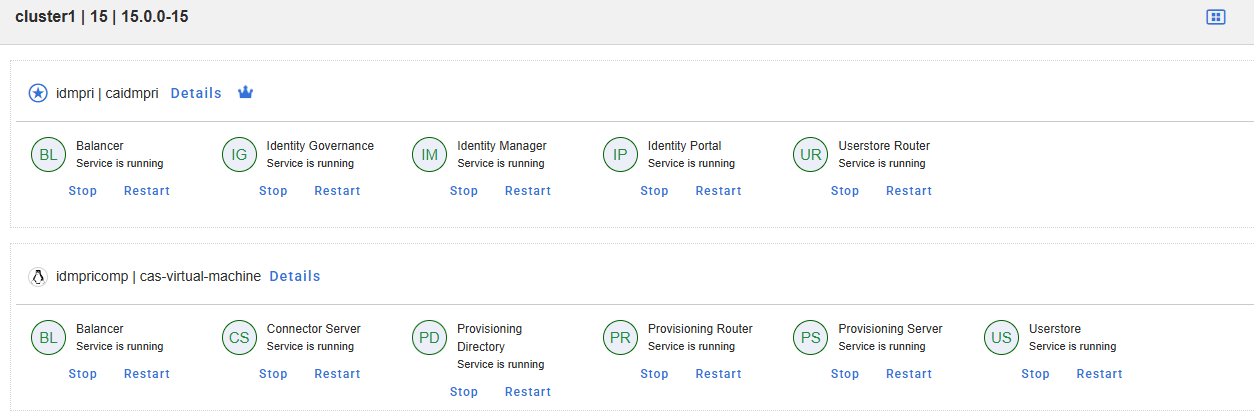
    I have already raised a support case (ID: 80035244), but it usually takes months before the actual problem is addressed. Maybe you can help.

    We are also facing another issue: we cannot connect to the Active Directory server through the C++ Connector Server. The out-of-the-box certificate eta2_servercert is issued to eta_server. In the Connector Xpress logs, we see an invalid hostname error:

    Java.net.URISyntaxException: Illegal character in hostname at index 11: ldaps://eta_server:20403/

    In Provisioning Manager, it also shows it cannot connect to ldaps://eta_server:20403/. I tried using a self-signed certificate, but it didn't work.

    Should I raise a separate support case for this issue, or wait until Identity Manager is working first?


    ------------------------------
    Network and security Engineer technical associative
    Cas Trading House
    Putalisadak, KTM
    ------------------------------


  • 4.  RE: IGA 15.0

    Posted Sep 12, 2025 01:34 PM

    Hi Sudip,

    The TLS port 20403 is used as you surmised by the C++ service on the MS Windows host.   

    Options you may wish to look at.

    The alias "eta_server" is typically reserved for the Provisioning Server.     While you could play host file tricks, it may break other lookup processes on the Provisioning server.

    The alias of "eta_server" is a placeholder that can be updated within the Provisioning Directory for the CCS connector true FQDN entry, if you access it with Jxplorer/Apache Dir Studio via TCP 20389/20390 on the Provisioning Host.

    If you search on the Broadcom site for the string "20403", you may find additional documentation that we created over the years.  Unfortunately, the documentation may have been indexed in other communities, e.g. Access Management (SSO/PAM)

    Visual Aid to Identity Suite Provisioning Tier Performance Updates | Symantec Access Management

    I have some additional notes on the C++ performance with Active Directory (below)

    https://anapartner.com/2021/05/24/parallel-provisioning-for-active-directory-and-ms-exchange-mailboxes-improve-birthright-dayone-access/


    Cheers,


    ------------------------------
    Alan Baugher
    ANA
    ------------------------------


  • 5.  RE: IGA 15.0

    Broadcom Employee
    Posted Sep 19, 2025 01:15 AM

    Sudip

    For adding CCS via ConXP, you must do one of the following

    1. Establish trust in ConXP trust-store. See import cert in https://techdocs.broadcom.com/us/en/symantec-security-software/identity-security/identity-manager/15-0/configuring/use-custom-certificates/Connector-Xpress.html
    2. You can disable SSL-verification. There is a SSL Verify option that you can uncheck.

    Instead of using ConXp, The IGA Xpress console has the facility to register CCS. 

    -------------------------------------------


  • 6.  RE: IGA 15.0

    Broadcom Employee
    Posted Sep 19, 2025 01:53 AM
    Edited by Laxminarayana Namani Sep 19, 2025 05:30 AM

    Hi Sudip,

    We can manage IMCS(JCS) using Connector Xpress but not CCS. Please use igx console to register CCS.

    Thank you.

    -------------------------------------------


  • 7.  RE: IGA 15.0

    Posted Sep 12, 2025 02:23 PM

    Hi Adrian,

    I always approach these migrations as an opportunity to reduce complexity and streamline processes.   

    Business processes are always updating, and it may be beneficial to retire or replace older processes while performing this effort.

    Unfortunately, the automation tools may move current configuration/data AS-IS and miss the steam-line opportunities.

    Example of some migration guidelines we have:

    Wish you the best.


    ------------------------------
    Alan Baugher
    ANA
    ------------------------------