I'm facing a strange issue with Automic agents running on Linux/Solaris.
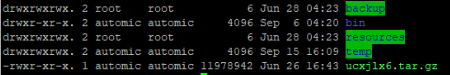
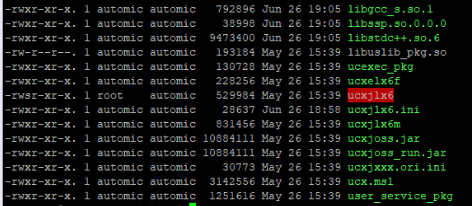
Normally, we have been setting the SUID bit (s-bit) and root ownership on the ucxjlx6 file for many years without any issues. This has been our standard configuration.
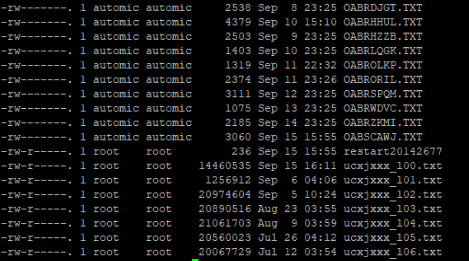
After upgrading to Agent 24.4.4 HF2, we noticed that the temporary log files created by the agent are now owned by root. As a result, we are unable to read these logs with the expected agent user permissions.
With earlier agent versions, under the same configuration and permission model (SUID bit (s-bit) and root ownership ), the temporary log files were owned by the Automic agent user, and we did not experience this issue.
It seems that something may have changed in this 24.4.4 HF2 version regarding log file creation or ownership handling.
Has anyone else encountered this behavior after upgrading to 24.4.4 HF2? If so, were you able to identify the root cause or find a workaround/solution?
Any insights would be greatly appreciated. Thanks!
------------------------------
Olgun Onur Ozmen
https://www.linkedin.com/in/olgunonurozmen/------------------------------