A Summer with CEM at Broadcom
Hi! I’m Carissa Lau, a junior studying Computer Science and Philosophy at the University of Illinois at Urbana-Champaign. This summer, I was invited to work with the Compliance Event Manager team.
Project Overview
Compliance Event Manager (CEM) protects businesses from data breaches, threat actors, and failed security audits through continuous mainframe security monitoring. CEM alerts users instantly to critical changes and security breaches, enabling immediate response and risk mitigation.
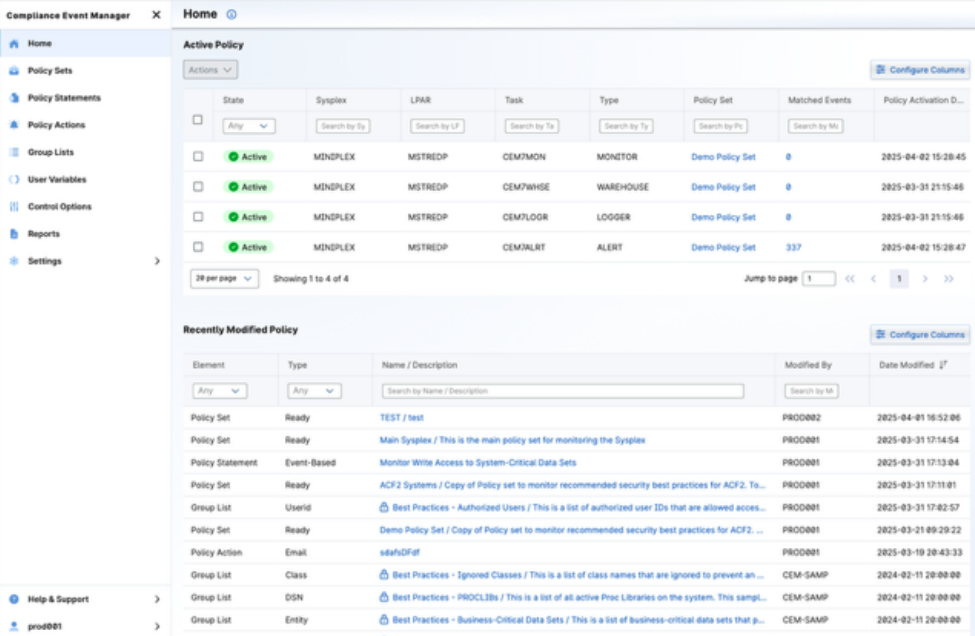
Fig. 1: CEM User Interface.
As a long-time user of Zowe, the open-source API mediation layer, the Compliance Event Manager (CEM) team prioritized reaching Zowe conformance. This certification is a milestone in modernizing CEM’s architecture and enhancing the platform’s security and usability.
To support this initiative, I was tasked with validating CEM’s REST API endpoints. This role required a disciplined approach to testing, as it is a highly critical step in aligning with the rigorous architectural standards required by the Zowe Conformance Program.
Process & Tools Used
My testing workflow centered on three key pillars: development, automation, and integration. To achieve Zowe conformance, I adopted an iterative approach for every REST API endpoint I tested.
-
Designing Test Scenarios in Bruno
I wrote and organized the majority of my test cases in Bruno, an open-source, git-friendly client used for testing and exploring APIs. Bruno stores API collections locally, which allows the team to version control our test suite. Across my tests, I focused on ensuring possible exploits and security issues were handled correctly. Through systematic progress, I scaled our test suite from 41 to several hundred cases, ensuring more rigorous validation across all endpoints.
Some examples of test scenarios:
-
Happy path: A GET request with valid fields to an accessible endpoint should return the information requested, a status code of 200, and a confirmation message.
-
Error handling: A POST request with an expired authentication token to an endpoint should return a status code of 401 (unauthenticated) and a corresponding error message.
-
Peer Review
After the initial test suites, I collaborated closely with my team, conducting code reviews to enhance current test cases, devise solutions to any difficulties in testing, and refine our testing standards. This step was critical to ensuring my test cases were resilient, covered edge cases, and adhered to proper internal security compliance protocols.
-
Automation and Integration with Jenkins
Once validated in Bruno and across my team, I integrated these test cases into our Jenkins pipeline, which acts as the engine of our CI/CD process. I also documented new scenarios added and any notable findings.
-
Custom Endpoint Development
Alongside developing tests, I also had the opportunity to develop a custom endpoint. I wrote this feature in IntelliJ IDEA, leveraging its handy debugging tools. To manage the compilation of this endpoint, I utilized Gradle, which provided the flexibility needed to handle the project’s complex dependencies, and Groovy, for creating unit tests using the Spock framework.
What I Learned
Stepping into a professional engineering environment provided me with hands-on experience in Agile practices and the modern software development lifestyle. By actively participating in daily stand-ups, code reviews, and iterative sprints, I gained a deeper understanding of practical collaborative development. I acquired a solid foundation in API security and compliance, which are skills I know will be invaluable in my future career.
Special thank you to the CEM team and my buddy, who believed in me every step of the way. Thanks to their efforts, I will carry this wonderful experience in my heart throughout my career, where I hope to pay their mentorship forward.